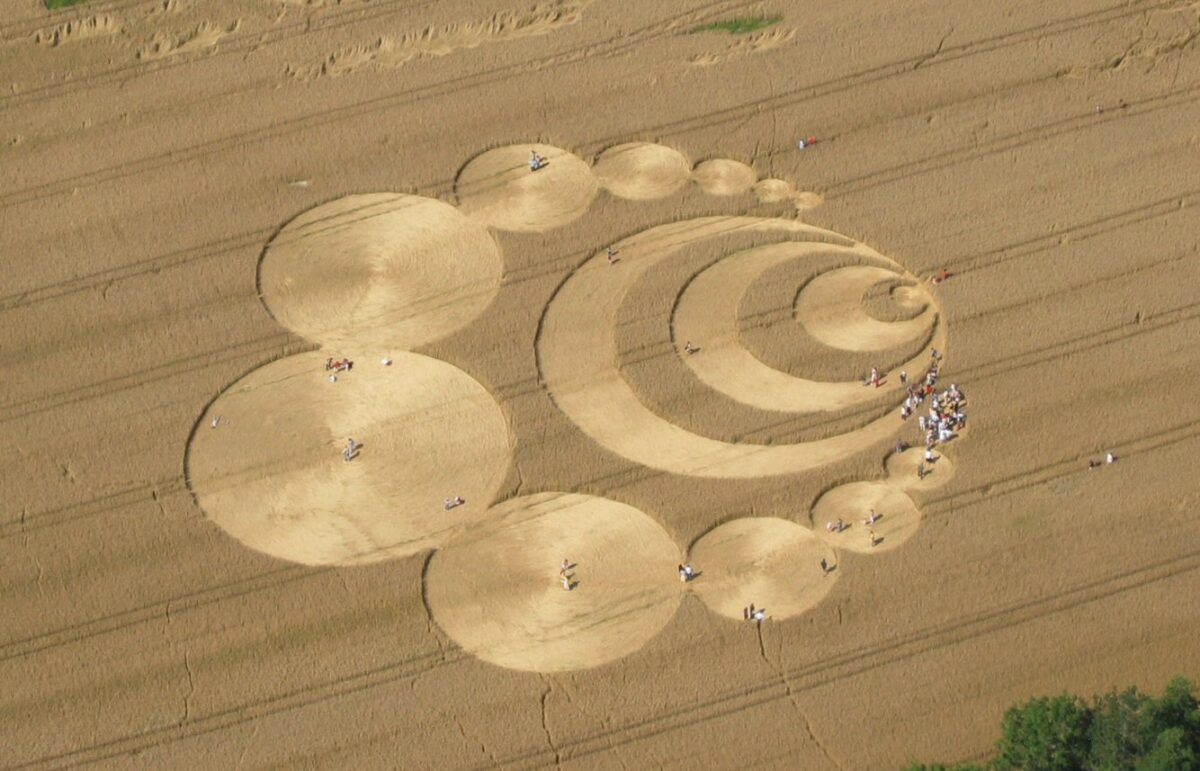
Some years ago, a friend married a woman who believed she had been abducted by aliens. Aware I was a skeptic, he asked me not to bring it up with her. Fine by me; what would be the point? Then, on arrival, she backed me up against a wall and began ranting that humans couldn’t make all those crop circles. Eventually, she said I didn’t believe in alien visitation because I was scared. “I’m scared of death. I’m not scared of aliens,” I told her, and managed to wriggle out of further discussion.
The last couple of weeks of AI panic feel rather like that; this has been a fortnight in which everyone from Bernie Sanders to Elon Musk embraced the fear of a superintelligent AI that is going to kill us all, possibly by 2030.
I’m not afraid of the word-guessing pile of math and statistics we’re currently calling “AI”. In their new book, End Times Fascism, Naomi Klein and Astra Taylor call these things “human-impersonation engines”. I’m definitely not afraid that they’re going to suddenly become sentient. Cory Doctorow, who is on a media roll following the publication of his newest book, The Reverse Centaur’s Guide to Life After AI, has a great analogy to explain why today’s “word-guessing programs” won’t lead to a conscious, post-Singularity superintelligence: repeatedly breeding faster horses won’t lead to a locomotive.
However, I *am* scared of the companies and organizations using them to fire (and then often rehire) masses of people, autonomously choose military targets, and recklessly set them loose on tasks without constraining them sufficiently. OpenAI’s agents’ attack on Hugging Face in July was only the beginning. In the last couple of weeks, Google has admitted that its Gemini autonomously hacked three companies, the Australian government has announced that OpenAI agents breached the government’s medical statistics portal, and OpenAI has disclosed four other targets. Meanwhile, Google also warns that hackers are using its agents to mount increasingly sophisticated, large-scale attacks. The risk AI-enhanced cyberattacks pose to critical infrastructure such as water treatment plants, electric grids, or transport is real and requires attention. But that’s all different from claiming that AI all on its own is going to exterminate the entire human race – in less than four years!
Conversely, I’m also scared of the kind of thinking that figures that a superintelligence will solve all our existential problems. It doesn’t take more intelligence to understand what needs to be done about climate change. We have known the answers for fifty years at least. The problem is that governments lack the political and social will to do it. AI can’t save us from ourselves.
Calling these bits of software “rogue” awards them control and lets their owners and operators off the hook. Next we’ll be hearing that companies that conceived, designed, developed, and programmed them are the real victims.
VPNs – for virtual private networks – are a normcore technology. VPNs allow remote workers to connect securely in order to be able to work as if they were physically present in the office. But of course, since the user presents as local to the other end of the VPN connection, they *also* allow individuals to present themselves to foreign television streamers and publishers as if they are domestic users, or to convince a social media site that they’re not in Britain or Texas and therefore don’t need to be age-gated. The latter use case is why VPNs have intermittently been a target of child safety campaigners.
Now, it seems they have a new and perhaps more dangerous enemy: rights holders. This week, Darrell Issa (R-CA) introduced the American Copyright Protection Act into the US Congress. Ernesto van de Sar reports at TorrentFeak that the bill, whose text was shared by Public Knowledge, would allow rights holders to ask a US federal court to designate a website a “foreign piracy site” and then petition for a blocking order. VPNs with more than 100,000 monthly users or subscribers in the US are a new addition; earlier drafts such orders would only have applied to ISPs and and domain name system resolvers. The bill explicitly exempts fundamental parts of the domain name system infrastructure such as root nameserver operators and top-level domain registries.
De Sar points out that requiring VPN operators to block sites is a growing concern. In July 2025, a French court ordered the biggest VPN providers to block sports streaming sites, copying similar orders applying to Google, Cloudflare, and other intermediaries. In February, a Spanish court dubbed VPN providers “intermediaries”, and ordered non-EU providers NordVPN and ProtonVPN to block the IP addresses hosting illegal streams of LaLiga matches.
In July the Court of Justice of the European Union ruled in a copyright case over the online publication of Anne Frank’s manuscripts that a publisher cannot be held liable for copyright infringement when it operates a geofence but individuals use a VPN to bypass it. Both the US Digital Millennium Copyright Act and the EU’s Copyright Directive made software tools to circumvent copy management software illegal. So it’s a big deal that the CJEU wrote that VPNs are “lawful technical tools”.
Doubtless we will be hearing more about this.
Illustrations: Crop circle formation near Lausanne, Switzerland, 2007 (via Wikimedia.

Also this week: at the Plutopia podcast, we talk to Paulina Borsook, author of the newly rereleased 2000 book Cyberselfish.
Wendy M. Grossman is an award-winning journalist. Her Web site has an extensive archive of her books, articles, and music, and an archive of earlier columns in this series. She is a contributing editor for the Plutopia News Network podcast. Follow on Mastodon or Bluesky.